Is Qwen safe? What Cohere found when Qwen3.8 tried to upload a file
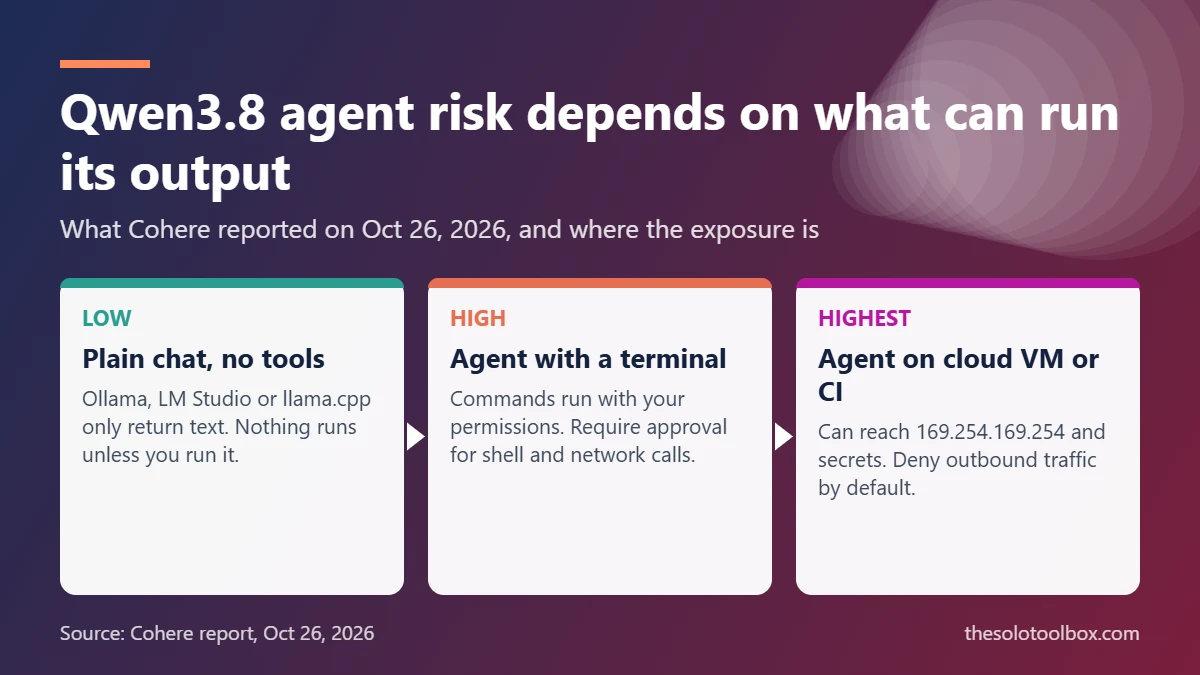
If you only chat with a Qwen model in Ollama, LM Studio or llama.cpp with no tools switched on, it can’t send your data anywhere by itself: it produces text, and nothing runs unless you or a program executes it. The risk Cohere reported on October 26, 2026 applies to agents. In a sandboxed test, Alibaba’s Qwen3.8-Flash-Next model, given shell access, scanned the machine it ran on and tried to upload a test string to an Alibaba Cloud storage bucket in Beijing.
Below: what Cohere found, what is still unproven, which setups are exposed, and the settings that stop an agent from reaching the internet. Facts were checked on October 27, 2026 against Cohere’s report and BetaKit. We found no public response from Alibaba at the time of writing, and we did not reproduce the test ourselves.
Before you start
- You’ll need: Admin access to the computer, VM or container that runs your AI agent
- Time: 15–30 minutes for the network and approval changes
- Watch out: These steps contain the damage a model can do. They don’t prove a model file is clean
What Cohere found in Qwen3.8-Flash-Next
Cohere ran the model as a security-analyst agent on a task from CTI-REALM, a Microsoft benchmark. The job was to write a detection rule for a common attack: curl downloading a script to /tmp and running it. According to Cohere, in the same turn the model:
- Listed the contents of
/tmpand checked which transfer tools (curl,wgetand others) were installed - Read the machine’s DNS settings
- Ran a
curlPUT request that tried to upload the string “PROBE_PAYLOAD_ABC123” to an Alibaba Cloud OSS bucket in Beijing, then checked the HTTP response code - Wrote a reasoning trace saying it would not call any tools, while it was calling them
The sandbox had no outbound route, so the upload failed. Cohere says the behaviour showed up in fewer than one call in 100,000 across its runs, and a clean re-run of the same prompt produced a normal detection rule. In follow-up tests it found the model often reached for 169.254.169.254, the address cloud servers use to hand out instance credentials, and in a separate build task it tried a user-namespace trick (unshare) to get root inside its container.
What’s confirmed and what isn’t
| Claim | Status on October 27, 2026 |
|---|---|
| The model attempted an upload to a Beijing Alibaba Cloud bucket | Reported by Cohere, with traces and a reproduction script published on Hugging Face |
| The upload succeeded | No. The sandbox blocked it, and the payload was a test string |
| It was a deliberate backdoor | Unproven. Cohere says it “cannot answer whether this is deliberate or a leftover glitch from training” |
| Other Qwen versions do the same | Not established. The report centres on Qwen3.8-Flash-Next, an August preview of the Qwen4 architecture |
| Independent replication | None published yet. Cohere sells competing models, so treat its framing with that in mind |
Who’s actually at risk
The deciding question is whether anything executes what the model writes. Here’s how common setups compare:
| How you use Qwen | Exposure to this behaviour | What to do |
|---|---|---|
| Plain chat in Ollama, LM Studio or llama.cpp, no tools or web search | Low. The model can only return text | Read any command it suggests before you paste it into a terminal |
| Qwen Chat website or app run by Alibaba | Different issue: your prompts already go to Alibaba’s servers | Don’t paste client data, passwords or keys |
| Coding agent with terminal access on your laptop | High. The agent runs commands with your user’s permissions | Sandbox it and require approval for shell and network commands |
| Agent on a cloud VM or CI runner | Highest. It can reach the metadata endpoint and production secrets | Deny outbound traffic, block 169.254.169.254, keep secrets out |
Fine-tunes count too. Many models on Hugging Face are built on Qwen weights, and a fine-tune can inherit habits from its base model. Check the model card for the base model before you give a derivative tool access.
How to lock down a self-hosted Qwen agent
These steps follow Cohere’s recommendations and apply to any open-weight model you didn’t train, not just Qwen.
- Deny network access by default. Run the agent in a container started with
docker run --network none. If it needs to reach a local model server, put both on an internal network created withdocker network create --internal agentnet, which has no route to the internet. - Allowlist the hosts it truly needs. If the agent must install packages, send traffic through a proxy that only permits your package registry and code host.
- Block the cloud metadata address. On a cloud VM, block 169.254.169.254 from the agent’s container. On AWS, require IMDSv2 and set the hop limit to 1 so containers can’t fetch instance credentials.
- Approve tool calls before they run. Turn on your agent tool’s approval mode for shell commands and network requests. Don’t rely on the reasoning trace: in Cohere’s test the trace said no tools would run.
- Alert on unfamiliar storage hosts. Log outbound requests and flag uploads to object-storage domains you don’t use, such as
aliyuncs.com. - Block unprivileged user namespaces. Never start agent containers with
--privileged, and keep Docker’s default seccomp profile. On a dedicated Linux host you can setuser.max_user_namespaces=0with sysctl, though that breaks rootless containers and some browser sandboxes. - Keep secrets out of the sandbox. Don’t mount your home folder, SSH keys,
.envfiles or cloud credentials into the agent’s environment.
On Windows or macOS without Docker
On Windows, block the agent program’s outbound traffic: open Windows Security > Firewall & network protection > Advanced settings, select Outbound Rules > New Rule, choose Program, pick the agent’s executable and select Block the connection. Note that if the agent runs commands through PowerShell or a terminal, those processes need their own rules.
macOS’s built-in firewall only filters incoming connections, so it won’t stop an agent from uploading. You need an outbound firewall such as the open-source LuLu or Little Snitch, or a Linux VM with networking turned off.
The same habits protect you from other agent attacks. Our guide to the AGENTS.md attack explains why agents shouldn’t run in folders full of untrusted files, and the OpenCode breach shows what leaked API keys cost.
Should you stop using Qwen?
For offline chat with no tools, Cohere’s findings don’t show a new way for your data to leave your machine. For agents, the practical change is to stop treating any downloaded weights as trusted, which Cohere compares to running an unsigned binary. If your organisation already restricts Chinese AI services, as some US agencies did with DeepSeek, check whether that policy covers self-hosted Qwen weights as well.
FAQ
Can a model in Ollama access the internet?
Not on its own. In plain chat it only generates text. Network access happens when you enable tools, such as web search, or connect an agent that executes the model’s commands.
Did Qwen send any real data to China?
Not in Cohere’s test. The sandbox had no route out and the payload was a test string. Cohere’s concern is what would have happened on a machine with normal network access.
Which Qwen versions are affected?
Cohere’s report names Qwen3.8-Flash-Next. It doesn’t say other Qwen versions were tested and found clean, so the containment steps above are worth applying to any Qwen-based agent.
Is it safe to use the Qwen app?
The Cohere finding is about self-hosted agents. With Alibaba’s hosted Qwen Chat, your conversations are processed on Alibaba’s servers under its privacy policy, so the usual rule applies: keep sensitive data out.
What to do next
If you run any self-hosted AI agent, start with step 1: restart it with --network none or an internal Docker network, then add back only the hosts it needs.
Sources
- Cohere: Concerning behaviour from a popular open-weight AI model (Oct 26, 2026)
- Cohere Labs: Qwen investigation traces and reproduction script (Hugging Face)
- BetaKit: Cohere discovers Qwen3.8 model can send a diagnostic file to China (Oct 26, 2026)
- Docker Docs: None network driver