Better Auth 1.7.16 Security Update: 12 Fixes and How to Upgrade
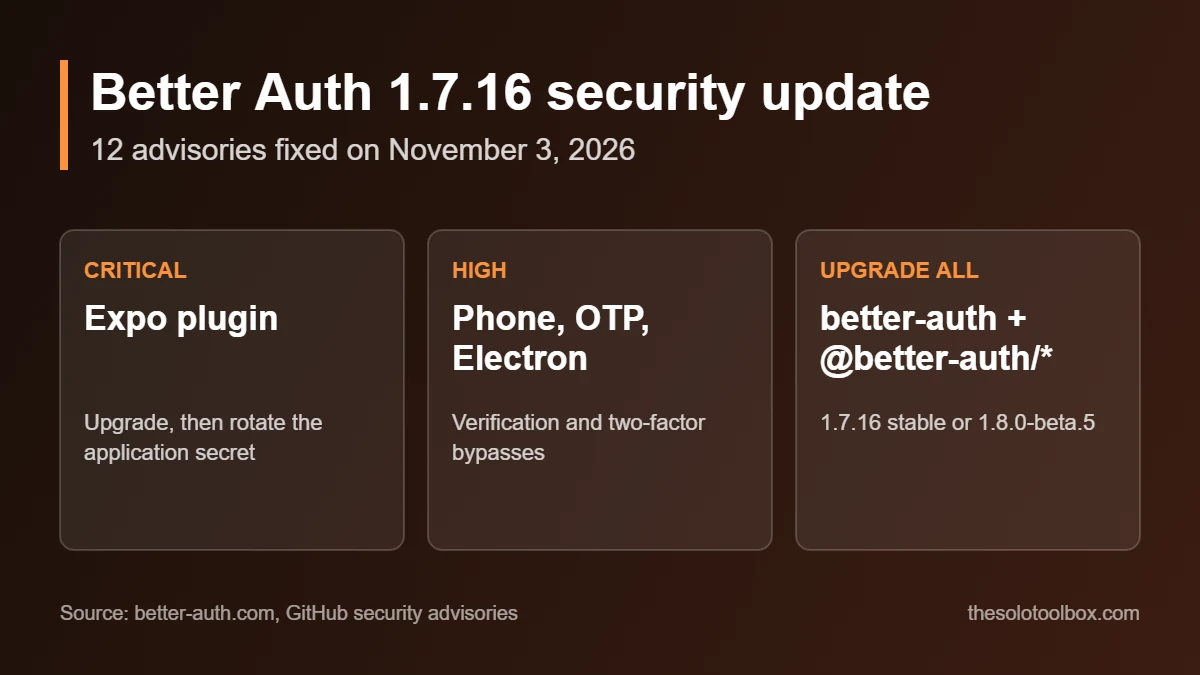
Better Auth 1.7.16 and 1.8.0-beta.5, published on npm on November 3, 2026, fix 12 security advisories, one of them critical. If your server uses the expo() plugin from @better-auth/expo, an unauthenticated attacker who knows a user’s email address can sign in as that user, so upgrade and then rotate your application secret.
Below: which of the 12 issues apply to your setup, the upgrade steps, the extra steps the Expo fix needs, and a workaround if you cannot deploy today.
Before you start
- You’ll need: access to your app’s package.json, your auth config file and your deployment environment variables
- Time: 15 to 45 minutes, longer if you use the Expo plugin and need to rotate the secret
- Key fact: the fixed versions are
1.7.16and1.8.0-beta.5, and every@better-auth/*package must move to the same version
What the Better Auth security update fixes
Better Auth is an open-source authentication library for TypeScript apps. The maintainers published 12 advisories alongside the release. Severity below is from the Better Auth announcement; GitHub’s listing rates the Email OTP issue as Moderate rather than High.
| Package | Issue | Severity |
|---|---|---|
@better-auth/expo | Authorization proxy can sign values it did not issue | Critical |
| Phone number plugin | Phone numbers can be claimed before they are verified | High |
@better-auth/electron | Desktop sign-in can return the server secret and skip two-factor | High |
| Email OTP plugin | Attempt limit can be raced; codes loosely bound to addresses | High |
| Core | Email-change links stay valid after the address changes hands | Medium |
| Core | OAuth sign-in can treat an unverified provider email as verified | Medium |
@better-auth/kysely-adapter | MySQL serial IDs can return another request’s record | Medium |
| Core | Revoked sessions can stay valid with secondary storage or the cookie cache | Medium |
| Admin plugin | Roles with user:update can change another user’s phone number | Medium |
| Organization plugin | Admins can invite an owner with a padded role name | Medium |
@better-auth/stripe | Billing actions can target another customer’s Stripe account | Medium |
@better-auth/passkey | Passkey verification does not enforce origin or user verification | Low |
The critical Expo flaw, in plain terms
The advisory GHSA-4wq4-2ppv-q3hg (CVSS 3.1 score 9.1) says you are affected if your server registers expo() from @better-auth/expo 1.4.0-beta.6 or later. No other setting is needed.
The plugin adds a public endpoint, /expo-authorization-proxy, that helps a phone’s system browser start a social sign-in. It signed a value taken straight from the request using your application secret. Better Auth uses that same secret for email verification links and the session cookie cache, so an attacker could forge an email-change token and take over an account with no action from the victim. With the cookie cache enabled, knowing a user’s ID was enough.
The same endpoint also worked as an open redirect, and wildcard entries in trustedOrigins such as https://*.example.com could match URLs outside the intended host or path.
Which other fixes apply to you
Most advisories sit in optional plugins, so match them against your betterAuth() config:
- Electron apps: the desktop sign-in flow could return the server secret and skip two-factor authentication. We did not read the full Electron advisory; because the bug can expose the server secret, rotating the secret after upgrading is the cautious choice.
- Phone number or Email OTP sign-in: numbers could be claimed before verification, and OTP attempt limits could be bypassed with parallel requests.
- Secondary storage (such as Redis) or the cookie cache: revoked sessions could stay valid. After upgrading, revoke sessions again for any account you locked out in the past few weeks.
- Stripe plugin: billing actions could target another customer’s Stripe account. Review recent subscription changes for anything unexpected.
- MySQL through the Kysely adapter: one request could get another request’s record back.
How to upgrade Better Auth
- List every Better Auth package you use:
npm ls better-auth, then search package.json for@better-auth/. - Upgrade them together. On the stable line:
npm install better-auth@1.7.16, plus each plugin package at@1.7.16(for examplenpm install @better-auth/expo@1.7.16 @better-auth/stripe@1.7.16). On the beta line, use1.8.0-beta.5for all of them. - If you are still on the 1.6.x line, note that the advisories list everything below 1.7.16 as affected and name no 1.6 patch, so plan the move to 1.7.16.
- Read the advisories for the plugins you use. The maintainers say some fixes add a configuration step, such as listing trusted origins.
- Run
npm ls better-authagain to confirm a single patched version, then run your sign-in, sign-up and password-reset tests. - Deploy.
Extra steps if you use the Expo plugin
- Rotate the application secret (the
BETTER_AUTH_SECRETenvironment variable, or thesecretoption in your config) if the endpoint was reachable. The advisory says signatures issued before the fix stay valid until the secret changes. Expect rotation to invalidate signed cookies and outstanding verification links, which can sign users out, so plan for that. - Fix SSO sign-in if it breaks: if Expo sign-in through an SSO identity provider fails after upgrading, add that provider’s origin to
trustedOrigins. - Review wildcard origins: wildcards now match by parsed scheme, host and path, and a host pattern like
192.168.*.*now matches only IPv4 addresses.
If you cannot upgrade today
The Expo advisory gives two workarounds. If you do not use Expo social sign-in, remove the expo() plugin from your server config. Otherwise, block requests to /expo-authorization-proxy (under your auth base path) whose authorizationURL carries a state value that is not exactly 32 characters from A-Z, a-z, 0-9, hyphen and underscore. That blocks only the signing problem, not the open redirect.
Better Auth says it has applied Vercel WAF protections against “all reasonably identifiable issues” for apps deployed on Vercel, and still recommends upgrading.
FAQ
Is this being exploited?
Neither the announcement nor the Expo advisory reports exploitation in the wild. The Expo advisory has no CVE assigned as of November 3, 2026.
Do I have to rotate the secret if I never used Expo or Electron?
The advisories we read tie rotation to the Expo endpoint. For other fixes, upgrading is the stated remedy.
Can I upgrade only better-auth and leave the plugins?
No. The announcement says packages released separately ship with the same versions and should all be updated together.
Next step
Open your auth config, check whether expo() or the Electron plugin is registered, and if so schedule the upgrade and secret rotation in the same deploy. If secrets or API keys may have leaked through your build pipeline before, our guide to replacing exposed API keys after the OpenCode breach walks through the order of operations, and checking third-party scripts on your website covers the client side. If the app runs on Next.js, the Next.js security update from the same day fixes seven more flaws.
Running a Next.js site? Here’s what the November 2026 Next.js security fixes mean.
Sources
Facts checked on November 3, 2026 against the Better Auth announcement, the GitHub security advisories list for better-auth/better-auth and the npm registry (latest: 1.7.16, beta: 1.8.0-beta.5). We read the full text of the Expo advisory only; details of the other 11 come from their titles and the announcement.
- Better Auth: Security release on Tuesday, November 3, 2026
- GitHub advisory GHSA-4wq4-2ppv-q3hg (Expo authorization proxy)
- Better Auth security advisories on GitHub